Identity-scoped routing
The demo endpoints were retired on 2026-07-31
/vip-ci and /vip-human on fusion.testsfapp.net are gone, together
with the second Cloudflare Access trust root they authenticated against —
a personally-owned issuer that no longer belonged on a tier now fronting a
real tenant. The pattern is unchanged and still current; only the
throwaway endpoints that demonstrated it were removed. The manifests
(authz-demo.yaml) remain in git history.
The capability: restrict a route to certain identities — certain people can
use certain routes, others get 403 — declaratively, with no service. The
mechanism is Envoy's native SecurityPolicy.authorization.
Foundation: Identity & traffic flow.
The flow
client → Envoy → [jwt: verify identity]
       → [authorization: match the VERIFIED claim against allow/deny rules]
       → 200 (allowed)  |  403 (denied)   → backend
Authorization runs after JWT verification and matches on the verified claim
(email, common_name, group), not on client headers — so unlike the ext_authz
header edge in upstream injection,
it is not spoofable.
Platform-supported method
defaultAction: Deny + an allow list keyed on the JWT claim:
kind: SecurityPolicy           # gateway.envoyproxy.io/v1alpha1
spec:
  targetRefs: [{kind: HTTPRoute, name: <your-route>}]
  jwt: { providers: [{name: cloudflare-access, ...}] }
  authorization:
    defaultAction: Deny
    rules:
      - name: allow-team
        action: Allow
        principal:
          jwt:
            provider: cloudflare-access
            claims:
              - {name: email, valueType: String, values: ["alice@example.com"]}
To pin an identity to a single route: allow it on that route, and rely on
defaultAction: Deny (or an absent allow entry) elsewhere.
Proof
The same caller (a service token) is allowed on one route and denied on another, purely by each route's authorization list:
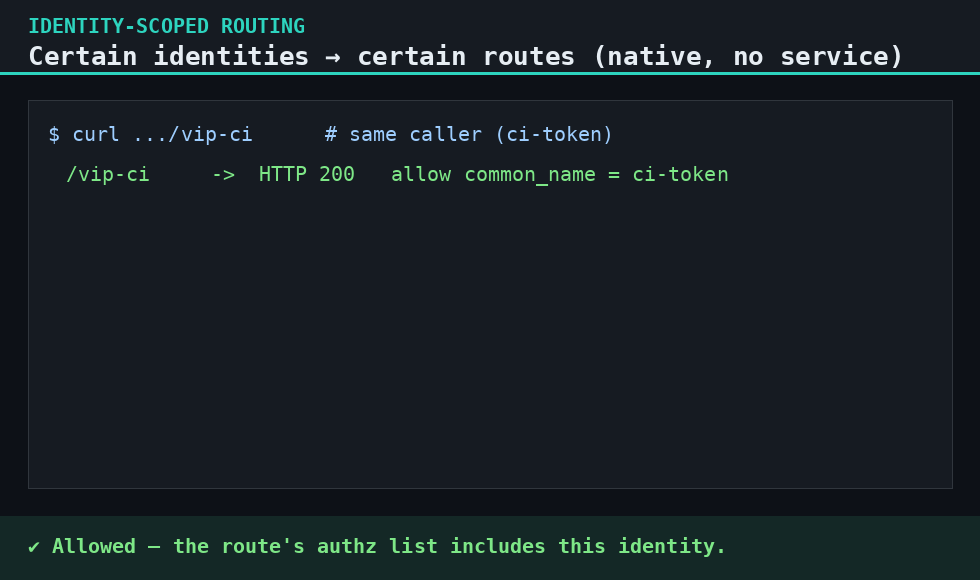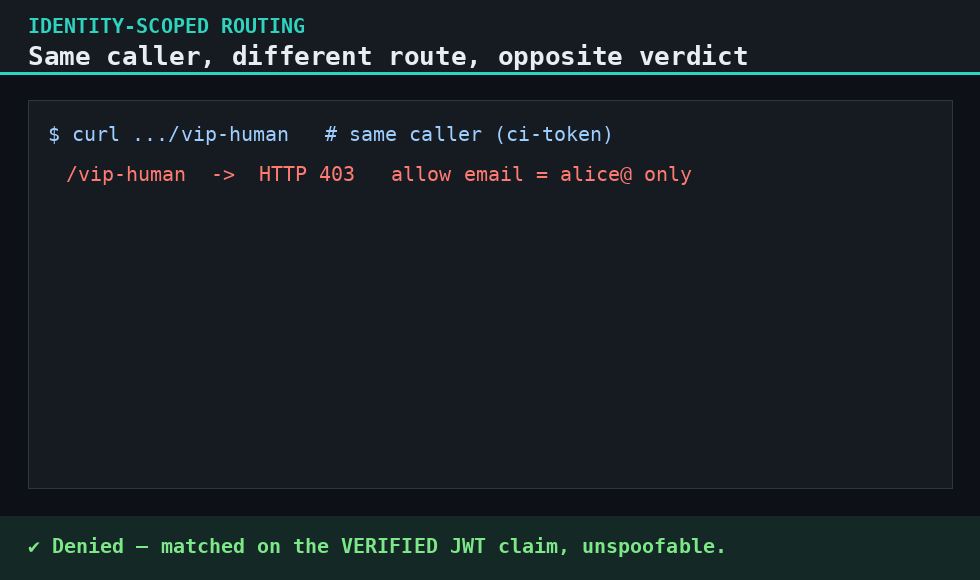
/vip-ciallows the token's verifiedcommon_name→ 200./vip-humanallows only a humanemail→ 403 for the token.
Security properties
- Unspoofable — matches the verified JWT claim, not a client header.
- Deny-by-default —
defaultAction: Denymeans a new identity is refused until explicitly allowed. - No service — pure gateway config; nothing to run or keep alive.
Sources: the gateway-patterns experiment (2026-07); live sf-fusion
SecurityPolicy.authorization; proof transcript.